Imagine that your product security team discovers credible evidence that an attacker is actively exploiting a vulnerability in one of your products.
The question is no longer simply:
“How quickly can we patch it?”
Under the EU Cyber Resilience Act, another question becomes equally important:
“How quickly can we report it?”
The Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, establishes specific reporting obligations for manufacturers of products with digital elements.
Stage 1: The First 24 Hours
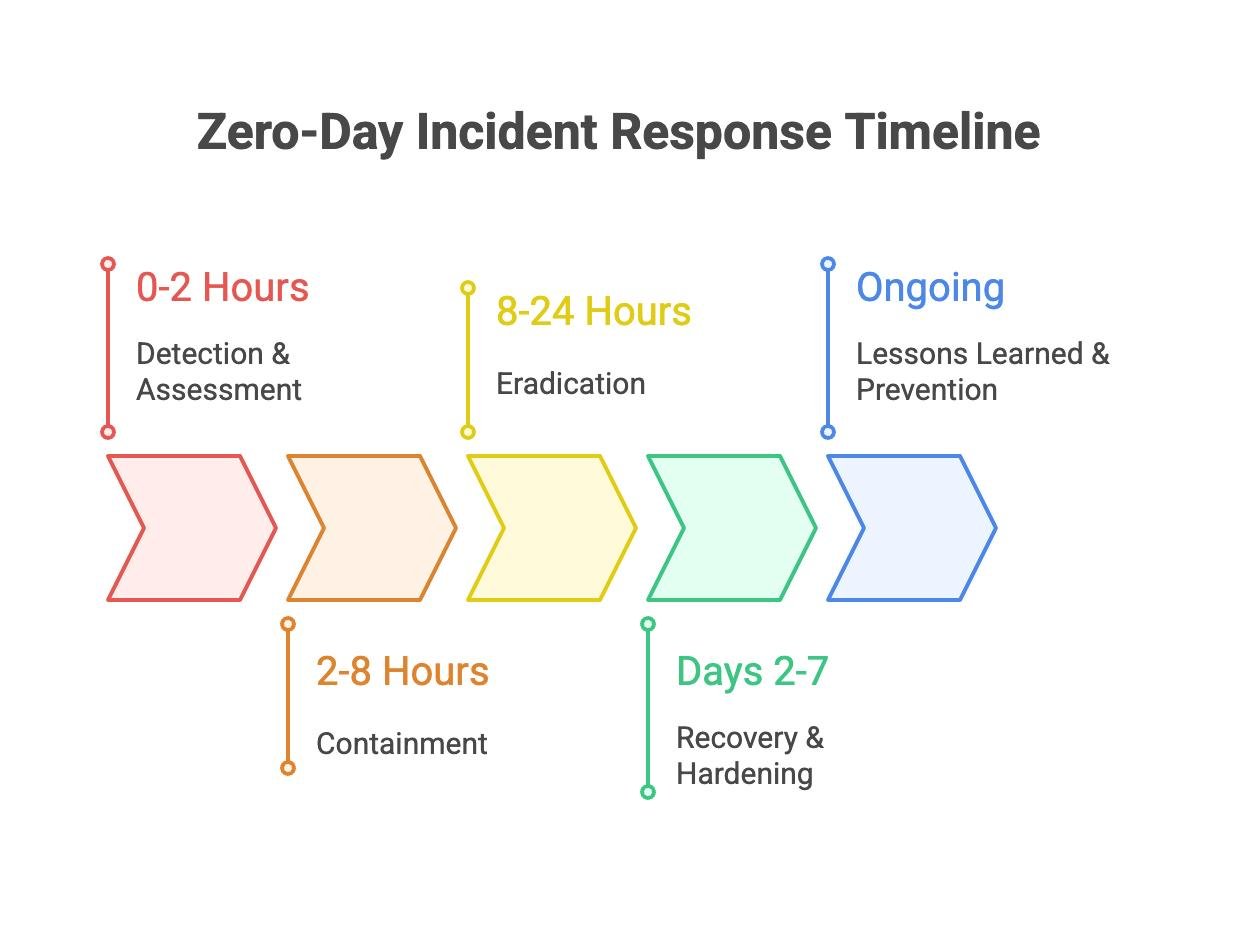
Once the manufacturer becomes aware of an actively exploited vulnerability, an early warning must be submitted without undue delay and no later than 24 hours.
At this stage, organizations should not assume they must have completed the entire investigation.
The purpose is early notification.
The organization needs an operational capability to quickly determine:
- What product is affected?
- What vulnerability has been identified?
- Is there evidence of active exploitation?
- Where is the product available?
- Who owns the incident?
- What immediate containment actions are required?
This requires close integration between vulnerability management, security operations, product security and incident response.
Stage 2: The 72-Hour Notification
Within 72 hours, the organization must provide additional information.
This includes available information concerning:
- The affected product
- The general nature of the exploit
- The vulnerability
- Corrective actions already taken
- Mitigation measures
- Actions users can take
- The sensitivity of the information, where applicable
This means organizations need an incident-response process capable of developing an initial technical assessment while the investigation is still evolving.
Stage 3: The Final Report
The final report has a different purpose.
It is submitted no later than 14 days after a corrective or mitigating measure becomes available.
The report should include:
- Vulnerability description
- Severity
- Impact
- Information about malicious actors, where available
- Security updates or other corrective measures
This creates an important distinction:
The final-report clock is not simply 14 days after the 24-hour notification.
It is tied to the availability of the corrective or mitigating measure.
What Security Teams Should Build
Organizations preparing for CRA compliance should consider implementing a dedicated CRA vulnerability-response playbook.
A practical workflow could look like this:
Detection
↓
Validate vulnerability
↓
Determine whether active exploitation exists
↓
Establish “awareness” timestamp
↓
Activate CRA reporting workflow
↓
24-Hour Early Warning
↓
Technical investigation and containment
↓
72-Hour Vulnerability Notification
↓
Develop corrective/mitigating measure
↓
Deploy security update
↓
Final Report within 14 days of corrective measure availability
The Most Important Control: Time Management
From a cybersecurity operations perspective, one of the most important controls will be the ability to establish and preserve the timeline.
Organizations should maintain evidence showing:
- When the vulnerability was discovered
- When it was validated
- When active exploitation was confirmed
- When management was notified
- When the CRA reporting process was initiated
- When the 24-hour notification was submitted
- When the 72-hour notification was submitted
- When mitigation became available
- When the final report was submitted
ENISA’s current CRA Single Reporting Platform guidance confirms the 24-hour, 72-hour and final-report workflow and provides operational guidance for submitting notifications.
The Technical Lesson
The CRA demonstrates that modern vulnerability management is no longer simply:
Find → Fix → Close
It is becoming:
Detect → Validate → Assess → Report → Contain → Remediate → Communicate → Evidence
That is a much more mature cybersecurity lifecycle.
References
- European Union, Regulation (EU) 2024/2847, Article 14.
- ENISA, Cyber Resilience Act Single Reporting Platform — Frequently Asked Questions, updated September 4, 2026.
- ENISA, Threats and Incidents — EU cybersecurity incident reporting context.